Community ranked
Crypto News
Written and ranked by the community. A manipulation-resistant algorithm surfaces what matters.
.jpeg)
FeaturedCrime
Crypto Launderers Shift Tactics, Moving Away from Centralized Exchanges, Chainalysis Reports
A new report from blockchain analysis firm Chainalysis reveals a significant shift in how illicit actors launder cryptocurrency. Launderers are increasingly abandoning centralized exchanges, which have bolstered their security and compliance measures, in favor of informal, service-based networks, particularly those operating through Chinese-language channels. This trend marks a notable evolution in the landscape of crypto-enabled financial crime. Key Takeaways Centralized crypto exchanges are seeing a decline in their use for money laundering. Informal networks, especially those using Chinese-speaking channels, are becoming dominant. These networks leverage money mules, informal OTC desks, and gambling platforms. The on-chain money laundering ecosystem has grown substantially, with billions laundered annually. Law enforcement faces a capability gap and needs to upskill to combat these evolving tactics. The Rise of Informal Networks Chainalysis data indicates that informal service-based networks, often facilitated through Chinese-speaking channels, have become the primary method for laundering illicit funds. These networks offer a diverse range of "laundering-as-a-service" options. They emerged prominently around the start of the COVID-19 pandemic in early 2020 and have since grown to "dominate known crypto money laundering activity." This shift away from centralized exchanges is attributed to increased regulatory scrutiny and enhanced security protocols on these platforms, making it harder for illicit actors to operate. Centralized exchanges can freeze funds, a risk that these informal networks aim to circumvent. Chinese-Language Networks Dominate Illicit Flows Over the past five years, Chainalysis estimates that Chinese-language networks have processed approximately 20% of all tracked illicit crypto funds. In stark contrast to the declining use of centralized exchanges, inflows to these identified Chinese-language networks have grown at an astonishing rate – 7,325 times faster than those directed to centralized exchanges since 2020. While not the sole facilitators of on-chain laundering, these Telegram-based services now account for a disproportionately large share of the global on-chain money laundering landscape. A Growing On-Chain Laundering Ecosystem The overall on-chain money laundering ecosystem has experienced significant expansion. Chainalysis projects that over $82 billion in illicit funds were laundered in 2025, a substantial increase from $10 billion in 2020. The Chinese-language networks alone were responsible for an estimated $16 billion, averaging roughly $44 million per day. This growth is fueled by the increasing accessibility and liquidity of cryptocurrencies, alongside a fundamental change in how and by whom this illicit activity is conducted. Law Enforcement Needs to Adapt Chainalysis emphasizes that law enforcement agencies must adapt their strategies to effectively combat this evolving threat. Disrupting on-chain money laundering requires targeting illicit operators, vendors, and their advertising platforms. Experts highlight a significant "chasm" in capabilities between criminals and law enforcement regarding cryptocurrency use in most countries. While blockchain tracing tools offer assistance, a more comprehensive, global effort is needed. This includes upskilling law enforcement personnel in crypto capabilities and establishing better information-sharing mechanisms worldwide. Sources Crypto launderers are turning away from centralized exchanges: Chainalysis — TradingView News, TradingView. Crypto launderers are turning away from centralized exchanges: Chainalysis, mx.advfn.com. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 37by Mini maNewcomer
.jpeg) Crime
Makina Finance Hit by $4.1M Exploit; MEV Bots Intercept Stolen Funds
Decentralized finance (DeFi) protocol Makina Finance has fallen victim to a significant exploit, resulting in the loss of approximately $4.13 million worth of Ethereum. The attack, which saw 1,299 ETH drained in a single transaction, was further complicated by the intervention of a Miner Extractable Value (MEV) builder that front-ran the attacker, capturing a portion of the stolen assets. Key Takeaways Makina Finance experienced a loss of $4.13 million in ETH due to a DeFi exploit. 1,299 ETH were drained in a single transaction. An MEV builder front-ran the attacker, capturing some of the stolen funds. The stolen assets are currently held in two separate wallets, with no further movement detected. Makina Finance has not yet issued an official statement regarding the incident. The Exploit Unfolds The security breach occurred on January 20, 2026, targeting Makina Finance's DUSD/USDC Curve pool. On-chain data indicates the exploit was executed through a large swap on Uniswap V3, where approximately 4.24 million USDC was exchanged for 1,299.18 ETH. The transaction, confirmed on Ethereum block 24,273,362, was completed with a remarkably low gas fee of just over $0.50, suggesting a carefully orchestrated execution. The funds moved through several protocols, including Curve and Aave, before settling on Uniswap. Blockchain data reveals that over $5.1 million in USDC passed through these transactions as part of the swap, with some liquidity routed through Curve's DAI and 3Crv pools. MEV Bots Intervene Adding another layer to the incident, an MEV builder bot identified by the address starting with 0xa6c2 intercepted the stolen ETH shortly after it arrived in the attacker's wallet. This MEV activity, occurring during the block-building stage, suggests the transaction was detected and acted upon before the primary attacker could move the funds further. While the MEV builder captured a small portion, approximately 0.13 ETH, it highlights the increasingly competitive and aggressive nature of trading on the Ethereum network. Current Status of Stolen Funds Following the exploit and the MEV builder's intervention, the stolen ETH remains split between two wallet addresses. One wallet holds approximately $3.3 million, while the other contains roughly $880,000. As of the latest reports, these funds have not been moved, mixed, bridged, or sent to any exchanges, providing a clear on-chain trail for investigators. Makina Finance's Silence Despite the significant financial loss and the public attention drawn by the exploit, Makina Finance has yet to release an official statement. The protocol's team has not acknowledged the incident on social media or provided any clarification on whether user funds were affected or if recovery efforts are underway. This silence is notable given the scale of the hack and the speed at which it occurred. The incident serves as a stark reminder of the persistent vulnerabilities within the DeFi space, even with advanced protocols and security measures. Flash loan attacks continue to be a prevalent method for exploiting liquidity pools, and the involvement of MEV bots adds another complex dimension to on-chain security. Sources Makina Finance Exploit Drains 1,299 ETH in Major DeFi Hack, The Crypto Times. MakinaFi Exploit Drains $4.1M as MEV Bots Front-Run Transactions, Coinfomania. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 45by Mini maNewcomer.jpeg) Crime
Terraform Labs Liquidator Sues Jump Trading for $4 Billion Over Alleged Role in Terra Collapse
The administrator overseeing the liquidation of Terraform Labs has filed a massive $4 billion lawsuit against crypto market maker Jump Trading. The suit alleges that Jump Trading played a direct role in the collapse of the Terra ecosystem, enriching itself through illicit market manipulation and self-dealing, ultimately leading to devastating financial losses for thousands of investors. Key Takeaways Terraform Labs' liquidator, Todd Snyder, is suing Jump Trading for $4 billion. The lawsuit alleges Jump Trading engaged in market manipulation and self-dealing that contributed to Terra's collapse. Secret agreements between Jump Trading and Terraform are cited as evidence. Jump Trading denies the allegations, calling the lawsuit a "desperate attempt" to shift blame. Allegations of Direct Involvement Todd Snyder, the plan administrator for the Terraform bankruptcy, has accused Jump Trading, its co-founder William DiSomma, and former crypto division president Kanav Kariya of directly contributing to the downfall of Do Kwon's company. The lawsuit claims Jump Trading "actively exploited the Terraform Labs ecosystem through manipulation, concealment, and self-dealing that enriched Jump while financially devastating thousands of unsuspecting investors." Secret Agreements and Market Manipulation Court documents reveal that since 2019, secret agreements existed between Jump Trading and Terraform. One such agreement allegedly allowed Jump to purchase LUNA at a significantly reduced price of $0.4 when the market price was as high as $110. Furthermore, Jump Trading is accused of having an informal agreement to artificially support the TerraUSD (UST) stablecoin's peg to the dollar, concealing these actions from regulators and the community. When UST lost its peg in May 2021, Jump Trading allegedly intervened by purchasing UST to restore its value, misleading investors into believing the algorithm was responsible for the recovery. The lawsuit further claims that once the stablecoin's vulnerability was known, Jump Trading secured the removal of vesting periods in contracts, enabling them to sell LUNA monthly and profit, thereby exacerbating pressure on the token. Exploiting the Collapse Following the initial stablecoin failure, the Luna Foundation Guard's Bitcoin reserve was established under the control of Kwon and Kariya. When UST collapsed again in May 2022, nearly 50,000 BTC (approximately $1.5 billion at the time) were transferred from this reserve without clear written agreements. The lawsuit suggests that DiSomma's attempts to salvage the situation by seeking liquidity from other crypto companies backfired, as competitors began selling TerraUSD and Luna upon learning of the project's issues. Jump Trading's Response and Past Settlements A representative for Jump Trading issued a statement calling the lawsuit a "desperate attempt by Terraform Labs to shift blame and financial responsibility from the crimes committed by Do Kwon. We will vigorously defend against these baseless allegations." This legal action follows a separate settlement in December 2024, where Jump's subsidiary, Tai Mo Shan, paid $123 million to resolve claims related to transactions with Terraform in 2021. In 2023, the U.S. Securities and Exchange Commission (SEC) also brought similar accusations, stating Jump Trading earned approximately $1 billion from transactions involving UST. Broader Impact and Legal Ramifications The collapse of TerraUSD and LUNA in May 2022 wiped out an estimated $40 billion in value, triggering a wider market downturn and leading to the failures of several major crypto firms, including Three Arrows Capital. Do Kwon was sentenced to 15 years in prison in December 2025 after pleading guilty to fraud charges. Sources Jump Trading Accused of Direct Involvement in Terra’s Collapse, ForkLog. Jump Trading Sued for $4 Billion Over Terra Collapse, Phemex. Todd Snyder Files $4 Billion Lawsuit Against Jump Trading Amid Crypto Turmoil, Value The Markets. Terraform Liquidators Allege Jump Trading Helped Fuel Crypto’s Biggest Crash: Report, Yahoo Finance. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 25by Mini maNewcomer.jpg) Crime
Romania Blacklists Polymarket Over Illegal Crypto Betting Amid Election Wagers
Romania's National Office for Gambling (ONJN) has officially blacklisted Polymarket, a prominent prediction market platform, citing its operation as an unlicensed gambling entity. This move comes in response to a significant surge in crypto-based betting activity on the platform during the country's recent presidential and local elections, where trading volumes reportedly exceeded $600 million. Key Takeaways Romania's gambling regulator has banned Polymarket for operating without a license. The decision was prompted by a surge in crypto betting on election outcomes, with volumes exceeding $600 million. Regulators classify Polymarket's activities as "counterpart betting," falling under gambling laws. The platform is accused of lacking fiscal reporting, player protection, and AML oversight. This action aligns with similar restrictions imposed by other countries, including the US, Belgium, France, and Poland. Regulatory Concerns and Classification The ONJN has classified Polymarket's operations as "counterpart betting," a model where users wager against each other on the outcomes of future events. According to ONJN President Vlad-Cristian Soare, the technology used, whether blockchain or traditional, does not exempt the platform from gambling regulations. The regulator emphasized that the core issue is adherence to the law, not the underlying technology. Violations and Oversight Issues Authorities pointed to several violations by Polymarket, including a lack of essential mechanisms for fiscal reporting, player protection, and Anti-Money Laundering (AML) oversight. Despite Polymarket's branding as an "event trading" platform, the ONJN maintains that its structure, which involves users betting on uncertain outcomes and the platform taking a commission, legally constitutes gambling. Consequently, Romanian internet providers are now mandated to block access to the site. International Precedents and Polymarket's Response Romania's decision is not an isolated incident. Polymarket has faced similar regulatory scrutiny and actions in other jurisdictions. In 2022, the U.S. Commodity Futures Trading Commission (CFTC) fined the platform for operating unregistered derivatives markets, leading to restrictions for American users. Belgium, France, Poland, Singapore, and Thailand have also implemented measures to restrict or block access to Polymarket. Despite these challenges, Polymarket has continued to grow, securing significant investment. The platform is reportedly preparing for a limited relaunch in the U.S. focusing on sports markets, following a CFTC no-action letter. Sources Romania blacklists Polymarket for illegal crypto betting amid $600M election wagers — TradingView News, TradingView. Romania bans Polymarket as $15m wagered on election, SBC News. Polymarket blacklisted in Romania despite marketing as ‘prediction market - Casino, Tribuna.com. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 25by BishopNewcomer Crime
Meteora Co-Founder Accused of Orchestrating Crypto Scams with MELANIA and LIBRA Tokens
A collective lawsuit has been filed against decentralized exchange (DEX) Meteora and its co-founder, Benjamin Chou, alleging fraud in connection with the controversial meme tokens LIBRA and MELANIA. The plaintiffs claim that the defendants exploited the authority of real individuals and narratives, including a token associated with former First Lady Melania Trump and an Argentinian revival token, to legitimize what they describe as a coordinated liquidity trap. Key Takeaways Meteora co-founder Benjamin Chou is facing a fraud lawsuit. The suit alleges Chou and Meteora were involved in "rug pull" schemes using meme tokens like LIBRA and MELANIA. Defendants are accused of using public figures and narratives as a "smokescreen" for fraudulent activities. Kelsier Ventures, led by Hayden Davis, is implicated in marketing campaigns for the tokens. At least 15 tokens were allegedly launched and sold using a similar fraudulent scheme. Allegations of a Coordinated Liquidity Trap The lawsuit asserts that the defendants "borrowed authority" from real-life figures and narratives to lend credibility to fraudulent schemes. These public personas and brands were allegedly used as props to legitimize what was, in reality, a "coordinated liquidity trap." The plaintiffs argue that these public figures were merely a "smokescreen" for the fraudulent scheme orchestrated by Meteora and Kelsier Ventures, headed by Hayden Davis. Meteora and Kelsier Ventures' Role According to the legal documents, Kelsier Ventures was responsible for conducting marketing campaigns for the launch of these tokens. Benjamin Chou is described as being "at the center of the business," having assembled a team to execute the alleged fraudulent scheme. The plaintiffs claim that the defendants launched and sold at least 15 tokens using a similar modus operandi. The lawsuit specifically names five of these tokens: LIBRA, MELANIA, ENRON, TRUST, and M3M3. Previous Statements and Market Scrutiny In February, Benjamin Chou stated in an interview that neither he nor Meteora had received any tokens or possessed insider information related to the Libra project. He subsequently stepped down from Meteora in the same month following public outcry. This development follows a report by the Financial Times in May, which revealed that a small group of traders had profited $99.6 million by purchasing the MELANIA meme coin before its official announcement, raising further questions about market manipulation and insider trading within the cryptocurrency space. Sources Meteora co-founder accused of ties to MELANIA and LIBRA scams, ForkLog. Meteora Founder Accused of Using Melania Trump, Milei for $57M Memecoin Scam, yahoo!finance This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 34by ToTo BugelmanNewcomer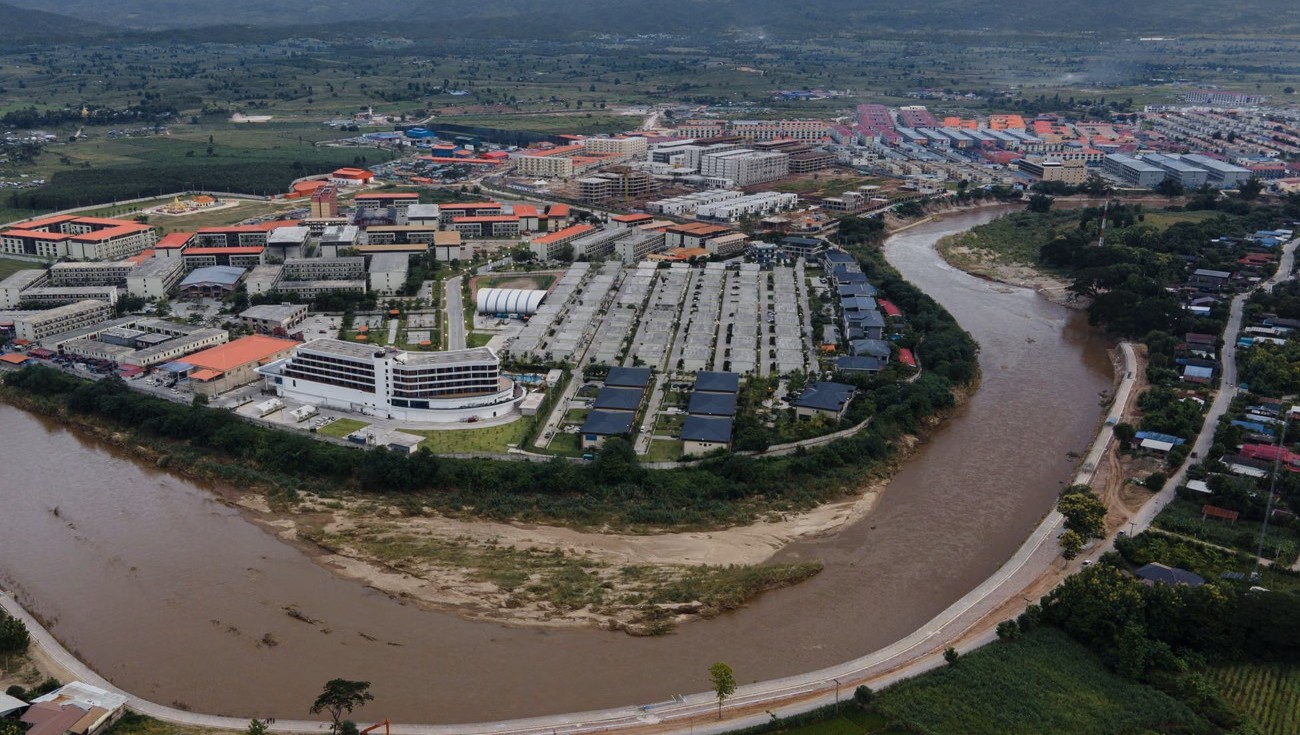 Crime
Myanmar Military Dismantles Major Cybercrime Hub, Rescues Over 2,000 Individuals
Myanmar's military has conducted a significant raid on KK Park, a notorious hub for cybercrime operations near the Thai border. The operation resulted in the arrest of over 2,000 individuals allegedly involved in online scams, illegal gambling, and cross-border cybercriminal activities. Authorities also seized a substantial amount of equipment, including dozens of Starlink satellite internet terminals. CNA Key Takeaways Over 2,000 individuals arrested in a raid on KK Park, a cybercrime center. Dozens of Starlink satellite internet terminals seized. Operations targeted online scams, illegal gambling, and cybercrime. Allegations of involvement by ethnic minority militia leadership. Crackdown on Cybercrime Operations The raid, part of an operation that began in early September, targeted KK Park, identified as a major center for cybercriminal activities. State media reported that the military confiscated equipment from over 260 unregistered buildings, including 30 Starlink satellite internet terminals. A total of 2,198 individuals were detained, though their nationalities were not specified. The scam operations are known to target victims globally, employing tactics such as building trust through online romance scams and fraudulent investment schemes. These centers often lure workers from other countries with false job offers, only to hold them captive and force them into criminal activities. International Context and Allegations This crackdown occurs amidst increased international attention on such criminal enterprises. Recently, the United States and the United Kingdom imposed sanctions on alleged organizers of a large cybercrime syndicate in Cambodia, with its purported leader facing federal charges in New York. KK Park is situated on the outskirts of Myawaddy, a key trading city on the Myanmar-Thailand border. The region is only partially controlled by the Myanmar military government and is also influenced by ethnic minority militias. Military government spokesperson Major General Zaw Min Tun accused the leadership of the Karen National Union, an armed ethnic organization, of involvement in the fraudulent schemes at KK Park. However, the group has denied any complicity. Starlink Equipment and Previous Actions Starlink, a service provided by Elon Musk's SpaceX, is not licensed to operate in Myanmar. Hundreds of terminals have reportedly been illegally imported into the country. SpaceX's policy prohibits "behavior that is defamatory, fraudulent, obscene, or misleading." Lauren Dreyer This is not the first time Myanmar has taken action against cybercrime. Earlier this year and in 2023, authorities have implemented measures against such activities. In February, under pressure from China, Thailand and Myanmar launched an operation that freed thousands of trafficking victims from underground camps. Liberation of People A raid by government forces allowed people who were effectively enslaved and forced to engage in criminal activities under threats to their health and lives to escape. Savanit Suriya Kul Na Ayutthaya, governor of Tak Province, told AFP that as of Thursday morning, 677 people had fled from KK Park across the Moei River into Thailand. According to the Thai army, among those detained were 618 men and 59 women. Most of them are citizens of India and China, with smaller numbers from Vietnam, Pakistan, Indonesia, and several other countries. Sources Thousands detained: Military launches major raid against online scammers, 365 дней. Myanmar military raids KK Park scam center, ForkLog Thousands detained as Myanmar military raids notorious KK park scam compound, Bangkok Post Myanmar scam centre raid sends hundreds fleeing to Thailand, Bangkok Post 2,500 scammer-linked Starlink rigs disabled in Myanmar, Bangkok Post This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 31by ToTo BugelmanNewcomer.jpeg) Crime
WazirX Secures Court Approval for Restructuring Plan Post-$234M Hack
The Singapore High Court has approved WazirX's restructuring plan, offering a path to recovery for users affected by a massive $234 million hack in July 2024. The plan aims to return a significant portion of lost funds through recovery tokens, which will grant holders a stake in future profits and any recovered assets. This approval marks a crucial step for the exchange to resume operations and begin compensating its customers. Key Takeaways Singapore High Court approves WazirX's restructuring plan. Plan aims to return 75-80% of stolen funds to affected users. Recovery tokens will offer profit-sharing and future fund recovery benefits. North Korea's Lazarus Group is blamed for the July 2024 hack. $3 million in stolen USDT has already been frozen. The Aftermath of the Hack In July 2024, WazirX fell victim to a sophisticated cyberattack, with North Korea's Lazarus Group identified as the perpetrators. The breach resulted in the loss of approximately $234 million in customer assets, leading the exchange to halt withdrawals. This event placed thousands of users in a difficult situation, prompting the need for a comprehensive recovery strategy. Court-Approved Restructuring Plan The Singapore High Court's approval of WazirX's restructuring plan provides a legal framework for the exchange to address the losses. Under the plan, WazirX will issue recovery tokens to affected users. These tokens represent a claim on future profits and any assets that may be recovered from the hack. The court found no evidence of WazirX's involvement in or responsibility for the hack, allowing the exchange to focus on recovery efforts. Fund Recovery Efforts Initial steps in fund recovery have shown promise, with $3 million in stolen Tether (USDT) successfully frozen. WazirX is collaborating with international law enforcement agencies in countries like the United States, Japan, and South Korea to trace and recover more of the stolen cryptocurrency. This multi-country investigation highlights the global nature of combating cryptocurrency crime. User Sentiment and Future Outlook While the court's decision is a significant step, some user groups have expressed concerns about the proposed timeline for the voting process, deeming it unnecessarily long. Despite these concerns, the overwhelming approval of the restructuring plan by creditors, with over 95% in favor, indicates a strong belief in the recovery process. WazirX aims to begin repayments within 10 business days of the plan's effective date, signaling a potential restart for the exchange and a path towards rebuilding user trust. Sources WazirX Restructuring Plan Gets Court Approval After $234M Hack, MoneyCheck. WazirX Creditors Approve Recovery Plan After $234M Hack, Live Bitcoin News. WazirX meets Singapore court deadline post-2024 hack, Cryptopolitan. WazirX Nears Comeback as Singapore Court Sets May Hearing on $234M Restructuring Plan, Decrypt. WazirX Restructuring Nears Final Hurdle with May 13 Court Hearing Date, CryptoRank. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 28by BishopNewcomer Crime
DeFi Protocol Hypervault Vanishes, Draining $3.6 Million in User Assets
The decentralized finance (DeFi) protocol Hypervault has reportedly disappeared, taking approximately $3.6 million in cryptocurrency assets with it. Security firm PeckShield first flagged suspicious outflows from the platform, indicating a potential "rug pull" scenario. The incident has left users questioning the security of DeFi investments. PeckShield Key Takeaways Hypervault has allegedly vanished with $3.6 million in crypto assets. Suspicious transactions were detected by security firm PeckShield. Assets were moved from Hyperliquid to Ethereum via a cross-chain bridge. The project's official website and X account are no longer accessible. The Disappearance PeckShieldAlert, a security monitoring service, reported significant suspicious withdrawals totaling around $3.6 million from the Hypervault DeFi platform on September 26, 2025. The stolen assets were initially transferred from the Hyperliquid network to the Ethereum network using a cross-chain bridge. Subsequently, these funds were converted to Ether (ETH). A substantial portion, approximately 752 ETH valued at around $3 million, was then sent to Tornado Cash, a privacy-focused cryptocurrency mixer commonly used in illicit activities and exit scams. What is a Rug Pull? A "rug pull" is a type of exit scam in the cryptocurrency space where the developers of a project abruptly abandon it, taking with them investors' funds. This often occurs after aggressive promotion of high yields or in the absence of thorough security audits. The pattern observed with Hypervault, including the movement of funds to a privacy mixer and the subsequent disappearance of the project's online presence, strongly suggests this type of fraudulent activity. Hypervault's Operations and Online Presence Prior to its disappearance, Hypervault's website and documentation promoted features such as "management-free" auto-compounding, yield-farming bots, and "adapters" designed to redirect assets into lending protocols, cyclical strategies, and concentrated liquidity pools on HyperEVM. These mechanisms were intended to distribute user deposits across various external services to generate complex income streams. However, the project's official X account has been deleted, and its website is now inaccessible, further fueling suspicions of an exit scam. The lack of accessibility and the suspicious fund movements paint a grim picture for investors who entrusted their assets to the protocol. Hypervault Sources DeFi protocol Hypervault vanished with $3.6 million, ForkLog. DeFi protocol Hypervault vanishes after $3.6 million suspected rugpull, The Block This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 34by ToTo BugelmanNewcomer.jpeg) Crime
FTX Fallout Continues: Ex-Exec's Plea Deal Dominates Latest Courtroom Drama
The legal repercussions from the collapse of cryptocurrency exchange FTX continue to unfold, with plea deals struck by former executives remaining a central focus in ongoing court proceedings. This week, Michelle Bond, the spouse of ex-FTX Digital Markets co-CEO Ryan Salame, is set to appear in court for an evidentiary hearing. Bond's Bid to Testify Amidst Salame's Plea Deal Michell Bond's legal team is pushing for her to testify in her criminal case, despite prosecutors' objections. The prosecution argues that Bond's testimony is unlikely to be relevant to Salame's plea agreement, which involves campaign finance fraud allegations. Salame is currently serving a prison sentence for his role in FTX's downfall. Bond's lawyers contend her testimony is crucial to understanding the state of mind of both her and her husband when entering the plea agreement. Salame's plea deal is at the core of Bond's case, which includes charges of conspiracy to cause unlawful campaign contributions and accepting excessive contributions. Prosecutors allege Salame directed $400,000 in FTX funds to Bond's campaign. Salame's Guilty Plea and Subsequent Legal Maneuvers Ryan Salame, one of five defendants indicted in the FTX and Alameda Research case, pleaded guilty to conspiracy charges related to operating an unlicensed money transmitting business and campaign finance fraud. He received a seven-and-a-half-year prison sentence. Following his guilty plea, Salame's lawyers attempted to withdraw the deal, claiming it was contingent on prosecutors not pursuing charges against Bond. This complaint was ultimately dropped, with Bond's case expected to address the matter. Potential Testimony and Prosecution's Stance The upcoming hearing is significant as it marks Bond's return to court after months of legal filings concerning Salame's plea deal. Bond's legal team has also requested the testimony of former Assistant U.S. Attorney Danielle Sassoon, who led the prosecution against Sam Bankman-Fried and other FTX executives. Sassoon's potential testimony aims to shed light on any promises or inducements made to Salame for his guilty plea. While the U.S. Attorneys have not opposed this motion, they have requested that Bond's lawyers provide supporting documentary evidence or testimony related to the plea deal. Sources Ex-FTX Exec’s Plea Deal Still at the Center of Court Case, Cointelegraph. Wife Of Former FTX Exec Says Charges Are Built On Deception, Law360. The Sam Bankman-Fried Trial: Full Coverage, CoinDesk. Fourth Top FTX Executive Pleads Guilty Ahead of Sam Bankman-Fried Trial, The New York Times. Sam Bankman-Fried’s day in court is nearly here. Who are the key players in the blockbuster trial of the former CEO of FTX?, Fortune. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 33by ToTo BugelmanNewcomer Crime
Sam Bankman-Fried's Appeal Hearing Set for November 4
Former FTX CEO Sam Bankman-Fried, currently serving a 25-year sentence, is set to have his appeal heard by the US Court of Appeals for the Second Circuit on November 4. This marks a significant development in his case since his transfer to a California correctional facility in March. His legal team is challenging his 2023 conviction and sentence, arguing he was denied the presumption of innocence and that prosecutors presented a misleading narrative regarding FTX user funds. Key Takeaways Sam Bankman-Fried's appeal hearing is scheduled for November 4. His legal team argues he was denied the presumption of innocence. A favorable ruling could lead to a new trial or sentencing. Bankman-Fried is currently serving a 25-year sentence. The Appeal Process Bankman-Fried's lawyers filed their notice of appeal in April 2024, following his conviction on seven felony counts and subsequent 25-year prison sentence in 2023. In their September 2024 appeal filing, his legal team contended that Bankman-Fried was "never presumed innocent" and that prosecutors created a "false narrative" suggesting FTX user funds were permanently lost. The outcome of this hearing could result in a new trial or a revised sentencing for the former FTX CEO. Background of the FTX Collapse The FTX exchange experienced severe liquidity issues and filed for bankruptcy in November 2022, leading to criminal charges against several of its executives. Bankman-Fried was the only senior executive to plead not guilty, resulting in a highly publicized trial. He was initially allowed to stay at his parents' home after extradition but had his bail revoked in August 2023 due to alleged witness intimidation. Sentencing of Associates Following Bankman-Fried's conviction, several of his associates have also faced sentencing. Caroline Ellison, former CEO of Alameda Research and Bankman-Fried's ex-girlfriend, received a two-year prison sentence after testifying against him. FTX co-founder Gary Wang and former engineering director Nishad Singh were sentenced to time served. Ryan Salame, former co-CEO of FTX Digital Markets, was sentenced to over seven years in prison after an attempt to vacate his guilty plea. The case of his partner, Michelle Bond, remains pending. Potential Presidential Pardon There have been reports suggesting that Bankman-Fried might be seeking a presidential pardon from US President Donald Trump. While he has signaled a willingness to align with Republican politicians, it remains uncertain if a pardon would be considered given the high public profile of his case. Sources US Court To Hear Arguments For Sam Bankman-Fried’s Appeal On Nov. 4, Cointelegraph. Sam Bankman Fried Faces November Appeal Hearing in New York, CryptoRank. Sam Bankman Fried Prepares for Appeal Hearing in November 2025, iGaming.org. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 24by ToTo BugelmanNewcomer.jpeg) Crime
US Crypto ATM Operator Accused of Facilitating Fraud, Targeting Elderly
Athena Bitcoin, a prominent US cryptocurrency ATM operator, is facing serious allegations from the Attorney General of Washington D.C. The company is accused of profiting from fraud schemes, particularly those targeting elderly individuals, and for failing to disclose exorbitant transaction fees. Investigations revealed a significant portion of funds processed through Athena's ATMs in the nation's capital were linked to fraudulent activities. Key Takeaways Athena Bitcoin allegedly processed a high volume of fraudulent transactions, with 93% of funds in its Washington D.C. ATMs linked to fraud in the first five months of operation. Customers in Washington D.C. were reportedly charged fees as high as 26%, with the markup concealed within the Bitcoin price. The company is accused of exploiting vulnerable adults and engaging in deceptive trade practices. Athena Bitcoin denies the allegations and states it has robust security protocols in place. Allegations of Fraudulent Practices The complaint filed by Washington D.C. Attorney General Brian Schwalb highlights that during the initial five months of operation in the capital, a staggering 93% of the funds deposited into Athena's ATMs were identified as originating from "outright fraud." This comes as Americans reported $189 million in losses to ATM-related fraud to the FBI in 2023. Exorbitant and Hidden Fees Schwalb's lawsuit further claims that customers in Washington D.C. were subjected to fees reaching up to 26%. This substantial markup was allegedly "baked into the price without disclosure to the consumer." In one documented instance, Athena sold Bitcoin at a price inflated by 25.4%. While the market price was $59,936, Athena's ATM offered it at $80,315. Consequently, for a $10,000 deposit, only $7,463 was transferred to the recipient, with Athena retaining $2,537. The prosecutor suggested that these fees might increase proportionally with the size of the customer's transaction. Exploitation of Vulnerable Adults The lawsuit also points out that Athena's ATMs feature "verbose warnings and complex legal disclaimers" that, in situations where victims are directed by scammers to deposit money, "exacerbate confusion and pressure." The company faces accusations of deceptive and unfair trade practices, as well as financial exploitation of vulnerable adults and the elderly. Athena Bitcoin's Defense A representative for Athena Bitcoin has strongly refuted the accusations, stating the company intends to defend itself vigorously in court. They emphasized that Athena employs stringent security protocols, including clear warnings about risks and ATM usage rules. "Our bitcoin ATMs are equipped with numerous safeguards, from prominent warnings and daily transaction limits to five separate verification screens designed to prevent coerced transactions and confirm that bitcoin is going to a wallet owned by [the customer]," the representative stated. Crypto ATM Landscape in the US According to Coin ATM Radar, there are currently 507 crypto ATMs operating in Washington state and a total of 31,019 across the United States. This case comes at a time when some countries, like New Zealand, are considering outright bans on crypto ATMs to combat money laundering. Sources US Crypto ATM Operator Accused of Facilitating Fraud, ForkLog. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 27by ToTo BugelmanNewcomer Crime
US Cracks Down on $10 Billion Crypto Scam Networks in Myanmar and Cambodia
The U.S. Treasury Department has imposed sanctions on 19 entities and individuals across Myanmar and Cambodia involved in massive cryptocurrency fraud schemes. These operations, which have grown significantly since Myanmar's 2021 military coup, have defrauded Americans of at least $10 billion in the past year, marking a 66% increase from the previous year. Treasury Department Key Takeaways The U.S. Treasury sanctioned nine entities in Myanmar and ten in Cambodia for orchestrating fraudulent schemes using cryptocurrencies. These scam centers are linked to human trafficking, forced labor, violence, and coercion. The total damage from these schemes in the region exceeded $10 billion in the past year. Myanmar Scam Hubs Targeted The sanctions specifically target operations in Shwe Kokko, Karen State, Myanmar, described as a notorious hub for virtual currency investment scams. These operations are allegedly protected by the Karen National Army (KNA), an ethnic militia group. Chinese businessman She Zhijiang and several associated firms, including Yatai New City, are among those sanctioned. Victims have reported being lured with false job offers, held against their will, and forced into illegal schemes under threat of physical harm. Cambodian Fraud Centers Sanctioned In Cambodia, sanctions were placed on four individuals and six organizations operating in Sihanoukville and Bavet. These entities are accused of running fraudulent complexes, initially built as casinos by Chinese investors, which transformed into centers for crypto investment scams. The illegal operations reportedly involved victims of human trafficking who were coerced into participating in scams and money laundering under threat of violence. Broader Impact and Coercion Tactics U.S. officials emphasized that the cyber scam industry in Southeast Asia not only threatens the financial security of Americans but also subjects thousands of people to modern slavery. The criminal networks often recruit workers under false pretenses, using debt bondage, violence, and threats of forced prostitution to coerce them into carrying out online fraud. The sanctions aim to disrupt these criminal networks by cutting off their funding and curbing their industrial-scale operations. Sources US Treasury Sanctions Crypto Fraudsters in Myanmar and Cambodia, ForkLog. US sanctions billion-dollar cyber scam networks in Myanmar and Cambodia, Reuters. Treasury Department targets Southeast Asia scam hubs with sanctions, CyberScoop. US sanctions online scam centers in southeast Asia, Anadolu Ajansı. US sanctions billion-dollar cyber scam networks in Myanmar and Cambodia, Latest news from Azerbaijan. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 32by ToTo BugelmanNewcomer.jpeg) Crime
SwissBorg Suffers $40 Million Hack, Affecting SOL Earn Program
SwissBorg, a prominent cryptocurrency platform, has fallen victim to a significant security breach, resulting in the loss of approximately $40 million worth of SOL. The incident, which occurred on September 8th, targeted the platform's SOL Earn product through a compromised partner API. While the main SwissBorg app and other 'Earn' programs remain secure, the attack has prompted swift action from the company to address user compensation. SwissBorg Key Takeaways Approximately 192,600 SOL, valued at $41 million, was stolen. The hack impacted the SOL Earn program via a compromised partner, Kiln, which provides staking infrastructure. SwissBorg assures that less than 1% of its user base was affected and that the core application is secure. A recovery plan is in place, with SwissBorg pledging to cover all user losses. Details of the Breach The attack was first brought to light by on-chain detective ZachXBT. Investigations revealed that the vulnerability stemmed from a compromised partner API belonging to Kiln, a service provider for Solana and Ethereum staking. SwissBorg has stated that the incident did not affect the overall security of its application or other 'Earn' programs, emphasizing that the company remains in a strong financial position and daily operations are unaffected. ZachXBT SwissBorg's Response and Recovery Plan In response to the breach, SwissBorg has outlined a comprehensive recovery plan. The company has committed to fully compensating all users who incurred losses due to the SOL Earn program exploit. This proactive approach aims to restore user confidence and mitigate the impact of the security incident. Broader Context of Crypto Security This incident at SwissBorg occurred on the same day that the DeFi platform Nemo, built on Sui, also experienced a security breach, with hackers making off with $2.4 million in USDC. The stolen funds were reportedly moved from Arbitrum to Ethereum. Nemo's team has temporarily suspended smart contract activity while investigating the cause, assuring users that assets in vaults are safe. These events highlight the persistent security challenges within the cryptocurrency ecosystem. Sources Attackers Hacked SwissBorg Crypto Platform and Stole $40 Million, ForkLog. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 31by ToTo BugelmanNewcomer.jpeg) Crime
Massive NPM Attack Yields Less Than $50 in Crypto Theft
A large-scale supply chain attack targeting popular JavaScript software libraries on the Node Package Manager (NPM) has resulted in minimal crypto theft, amounting to less than $50. Security researchers from Security Alliance revealed that hackers compromised an NPM developer's account, injecting malware into widely used libraries downloaded over a billion times. While Ethereum and Solana wallets were specifically targeted, the immediate financial impact appears to be surprisingly low, though the full extent of the damage is still being assessed. Josh Junon Key Takeaways A significant supply chain attack on NPM libraries has been detected. Hackers injected malware into popular JavaScript packages. Despite widespread potential impact, less than $50 in cryptocurrency was stolen. Ethereum and Solana wallets were the primary targets. The Attack Details Security intelligence platform Security Alliance reported that attackers gained access to the NPM account of a prominent software developer. They then inserted malicious code into several JavaScript libraries, including chalk, strip-ansi, and color-convert. These libraries are deeply embedded in numerous projects, meaning even developers who did not directly install them could be exposed. The malware deployed is identified as a crypto-clipper, designed to stealthily replace legitimate wallet addresses with the attacker's during transactions, thereby diverting funds. The compromised Ethereum wallet address, "0xFc4a48," is believed to be the sole recipient of the illicit funds so far. Minimal Financial Impact, High Potential Risk While the attackers had the potential to access millions of developer workstations, the actual crypto stolen was minimal. Initially reported as five cents, the amount later rose to approximately $50, comprising Ether (ETH) and various memecoins such as Brett (BRETT), Andy (ANDY), Dork Lord (DORK), Ethervista (VISTA), and Gondola (GONDOLA). Etherscan data confirms these transactions to the malicious wallet address. Security Alliance Industry experts, including Ledger's CTO Charles Guillemet, have advised users to exercise caution and double-check on-chain transaction details. DeFiLlama founder 0xngmi noted that only projects updating their dependencies after the malware was introduced are at risk, and users must still approve the malicious transaction for it to succeed. However, he recommended avoiding crypto websites until the affected packages are cleaned. This incident highlights the persistent threat of supply chain attacks in the software development ecosystem, particularly within the cryptocurrency space, even when the immediate financial losses are small. Sources Not Even $50 Of Crypto Stolen From Large-Scale NPM Attack, Cointelegraph. Largest NPM attack in crypto history stole less than $50: SEAL — TradingView News, TradingView. Not Even $50 Of Crypto Stolen From Large-Scale NPM Attack, Cointelegraph. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 26by ToTo BugelmanNewcomer Crime
Crypto Kingpin Alex Mashinsky Gets 12 Years for Defrauding Celsius Customers
Former Celsius CEO Alex Mashinsky has been sentenced to 12 years in federal prison for orchestrating a massive fraud scheme that cost investors billions. Mashinsky, once a prominent figure in the cryptocurrency world, will surrender to authorities this week, marking a significant downfall for the leader of a company that collapsed in 2022. Key Takeaways Alex Mashinsky, former CEO of Celsius Network, sentenced to 12 years in prison. Convicted of commodities fraud and manipulating the Celsius token. Prosecutors sought a 20-year sentence, highlighting a "deliberate and calculated" scheme. Victims reported devastating financial and emotional losses. A Dramatic Fall From Crypto Grace Alex Mashinsky, the former CEO of Celsius Network, has been handed a 12-year prison sentence after pleading guilty to two counts of fraud. The sentencing, delivered in Manhattan's Southern District Court, concludes a years-long legal battle that saw the once-celebrated crypto leader accused of misleading investors about the safety and profitability of Celsius's yield-generating platform. Prosecutors argued that Mashinsky engaged in a deliberate scheme to defraud customers, inflate the value of the Celsius token (CEL) using customer funds, and ultimately cost investors billions. SDNY The Celsius Collapse and Its Aftermath At its peak, Celsius managed over $20 billion in crypto assets, marketing itself as a secure alternative to traditional banking. However, behind the scenes, the company allegedly took on risky loans and used customer funds for speculative investments. The company filed for bankruptcy in July 2022, freezing approximately $4.7 billion in user funds. Mashinsky resigned as CEO shortly after. Celsius has since emerged from bankruptcy, beginning the distribution of assets to creditors. Mashinsky forfeited all claims to the company during the proceedings. Victim Impact and Sentencing Details Ahead of the sentencing, over 200 victim impact statements were submitted to the court, detailing severe financial devastation, mental health crises, and even suicides linked to Mashinsky's actions. Investors described losing their life savings, with some calling for a sentence comparable to that of Bernie Madoff. While prosecutors pushed for a 20-year term, U.S. District Judge John G. Koeltl imposed the 12-year sentence. In addition to prison time, Mashinsky will serve three years of supervised release, pay a $50,000 fine, and forfeit over $48 million. A Parallel to Other Crypto Executions Mashinsky's sentencing places him among other high-profile crypto executives who have faced legal consequences. Figures like Sam Bankman-Fried (FTX), Changpeng Zhao (Binance), and Do Kwon (Terraform Labs) have also been implicated in major fraud cases. Bankman-Fried is serving a 25-year sentence, Zhao received a four-month sentence, and Kwon awaits sentencing after a guilty plea. Sources Ex-Celsius CEO Set To Start 12-Year Prison Sentence This Week, Cointelegraph. Celsius CEO Alex Mashinsky sentenced to 12 years in crypto fraud case, CNBC. Celsius' Alex Mashinsky Dodges Maximum Term, Gets 12 Years Despite Prosecutors' 20-Year Plea, CCN.com. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 32by ToTo BugelmanNewcomer Crime
Germany May Have Missed Out on $5 Billion in Bitcoin from Piracy Case, Arkham Reports
German authorities may have overlooked a substantial stash of Bitcoin, estimated at $5 billion, linked to the defunct movie piracy site Movie2K. Crypto intelligence firm Arkham revealed that over 45,000 Bitcoin remain untouched in wallets associated with the site's operators, raising questions about the effectiveness of Germany's asset seizure strategies. Arkham Key Takeaways Arkham Intelligence identified over 45,000 BTC, valued at approximately $5 billion, still held in wallets linked to the Movie2K piracy site. These funds have reportedly remained unmoved since 2019 and were not part of Germany's previous seizure and sale of nearly 50,000 BTC. German authorities previously sold seized Bitcoin in mid-2024, a move criticized for potentially missing out on significant future gains as the cryptocurrency's price surged. Recovering the newly identified Bitcoin would require German authorities to prove its illicit origin in court and gain control of over 100 wallets. Unclaimed Bitcoin Stash Arkham's analysis indicates that 45,060 Bitcoin, currently worth close to $5 billion, are still held across more than 100 wallets connected to Movie2K. These digital assets have not shown any activity since 2019, suggesting they remain under the control of the original operators of the piracy website. Notably, these wallets were not mentioned in any official communications from German authorities regarding the Movie2K case. Previous Seizure and Sale In early 2024, German police seized nearly 50,000 Bitcoin as part of their investigation into Movie2K. These confiscated coins were subsequently sold by authorities between June and July 2024 for an average price of $57,900 per Bitcoin, netting approximately $2.8 billion. This sale occurred just months before Bitcoin's price experienced a significant rally, leading to criticism that German authorities missed out on potentially doubling their returns. Prosecutors had justified the swift sale by citing German laws that mandate the liquidation of volatile assets to mitigate the risk of value loss. However, the subsequent price surge has fueled debate about whether a different strategy, such as holding the assets, would have been more financially prudent. Legal Hurdles for Recovery For German authorities to seize the newly identified Bitcoin, they must first prove in court that the funds are indeed linked to Movie2K and constitute proceeds of criminal activity. Even if successful, the government would then need to locate and gain control of the private keys for over 100 separate wallets. This process could be lengthy and complex, potentially taking years to resolve, if it can be achieved at all. Debate Over Asset Management The discovery has reignited discussions among crypto advocates and lawmakers about how governments should manage confiscated digital assets. Some have suggested that Germany should consider holding seized Bitcoin as part of a sovereign reserve, potentially yielding long-term economic benefits rather than immediate cash injections. However, German central bank officials have expressed skepticism about Bitcoin's suitability for national reserves due to its volatility. Sources Germany Missed $5B Bitcoin in Piracy Case, Says Arkham, Cointelegraph. Germany May Have Missed Seizing $5 Billion in Bitcoin from Movie2K Case, Cryptonews. German authorities reportedly missed $5B in BTC from Movie2K case, CryptoRank. Arkham Finds $5B in Bitcoin Tied to Movie2K Still Unmoved Since 2019, CoinCentral. Germany Could Make a $5 Billion Bitcoin Comeback, BeInCrypto. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 28by ToTo BugelmanNewcomer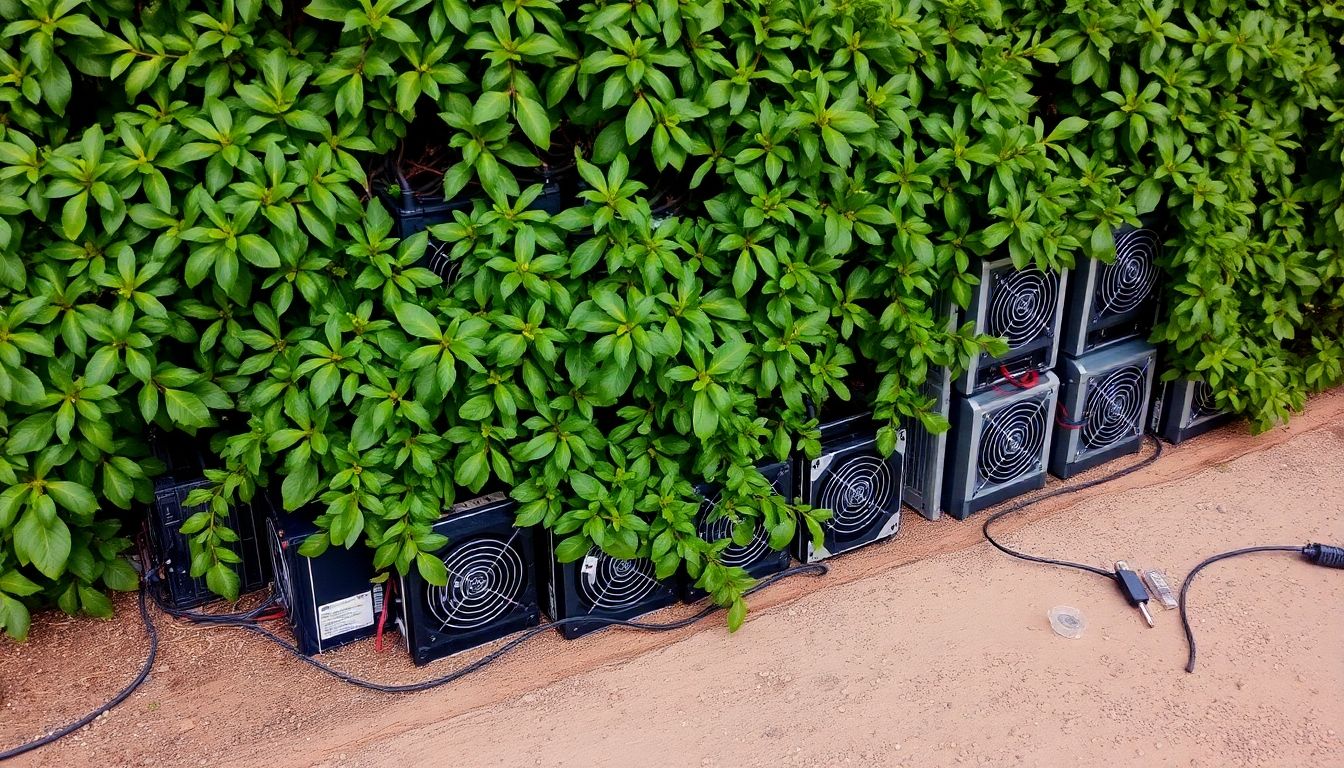 Crime
Hidden Mining Farm Uncovered in Irkutsk Bushes
Irkutsk police, in collaboration with energy company specialists, have discovered and dismantled an illegal cryptocurrency mining operation concealed within bushes on a vacant lot. The hidden farm, consisting of 21 ASIC mining devices, was illegally connected to a 0.4 kV power line, posing a significant risk and causing substantial financial damage. Svetpriangaria38 Key Takeaways An illegal mining farm with 21 ASIC devices was found hidden in bushes in Irkutsk. The operation was connected to a power line just 20 meters from residential buildings. Estimated monthly profits were around 250,000 rubles, with electricity theft causing approximately 1 million rubles in damages. Authorities are currently identifying individuals involved in organizing the illegal farm. Discovery and Operation Details Law enforcement officials and representatives from the "Irkutsk Electric Grid Company" (IЭСК) stumbled upon the clandestine mining farm while on patrol. The setup was discreetly placed in a wooded area, mere meters away from residential streets, highlighting a blatant disregard for public safety and regulations. The 21 ASIC mining units were directly tapped into a 0.4 kV power line, indicating a sophisticated but illegal setup. Financial Impact and Damages Preliminary assessments suggest that the illegal operation was generating an estimated monthly income of approximately 250,000 rubles. However, the cost to the local power grid was far more substantial. The unauthorized consumption of electricity resulted in an estimated damage of around 1 million rubles. This figure underscores the significant financial losses incurred due to the untaxed and unregulated energy usage. Regulatory Context and Ongoing Investigation This discovery comes at a time when Russia is tightening regulations around cryptocurrency mining. Since January 1st, the government has implemented stricter controls, with mining activities in most regions requiring registration and adherence to state oversight. Individuals are permitted to mine within a monthly limit of 6,000 kWh, provided they are registered. The authorities are actively working to identify and apprehend all individuals responsible for establishing and operating this illicit mining farm. The investigation is ongoing, with potential charges related to illegal electricity consumption and unauthorized business activities expected. Related Incidents This incident in Irkutsk is not isolated. Recently, four suspects were apprehended in the Irkutsk region for allegedly stealing mining equipment valued at 5.3 million rubles. In another case, a large mining farm in Krasnoyarsk was shut down after its operator expanded operations beyond leased premises, impacting power supply to essential facilities like a polyclinic. These events highlight a growing trend of illegal mining activities and the challenges authorities face in combating them. Irina Volk_MVD Sources Иркутская полиция обнаружила майнинг-ферму в кустах, ForkLog. В лесопосадке Иркутска ликвидирована нелегальная майнинг-ферма, Bits Media. Еще одну майнинговую ферму нашли в Иркутске — в кустах на пустыре - 2 сентября 2025, ИРСИТИ.ру. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 29by ToTo BugelmanNewcomer Crime
Millions Lost in Phishing Scam: Venus Protocol Pauses Operations Amidst Security Review
A significant phishing attack has led to a substantial loss of cryptocurrency for a user of the Venus Protocol, a decentralized finance (DeFi) platform. The incident prompted the platform to temporarily pause its operations to conduct a thorough security review. While initial reports indicated a loss of $27 million, the figure was later corrected to $13.5 million after accounting for the user's debt position. PeckShieldAlert Key Takeaways A Venus Protocol user lost $13.5 million in a phishing scam. The platform has paused operations for security reviews. No vulnerabilities were found in Venus Protocol's smart contracts. The incident highlights ongoing risks of social engineering in DeFi. The Phishing Attack The attack occurred when a user approved a malicious transaction, inadvertently granting an attacker token approval for asset transfer. This allowed the attacker to drain stablecoins and wrapped assets from the user's wallet. Blockchain security firm PeckShield initially reported the loss at $27 million but later revised it to $13.5 million, explaining that the initial estimate did not account for the user's existing debt within the protocol. Venus Protocol's Response In response to the incident, Venus Protocol confirmed that the issue was not due to a flaw in its smart contracts but rather a targeted phishing attack on the user. As a precautionary measure, the platform announced a temporary pause on its operations to conduct comprehensive security reviews. The protocol stated that operations would resume once the investigation is complete and justice is restored to the affected user. Venus Protocol UPD: Venus Protocole has resumed its work in full. Venus Protocol Broader Context of Crypto Scams This incident occurs amidst a broader trend of increasing crypto scams. In August, PeckShield reported that 16 major exploits resulted in over $163 million in losses across the crypto space, a 15% increase from July. Notable incidents included a Bitcoin investor losing $91.4 million and the Turkish exchange BTCTurk suffering a $54 million hack. These events underscore the persistent risks of social engineering and the importance of robust security practices for DeFi users, including careful transaction review and the use of hardware wallets. Sources Venus Protocol User Loses $13.5M in Phishing Attack, Cointelegraph. Venus Protocol User Loses $13,5 Million Due to Phishing Attack, Happy Coin News. Venus Protocol Halts Operations After $27M Phishing Loss, AInvest. Venus Protocol Paused After User Loses $13.5 in Phishing Scam, CCN.com. Crypto user loses $27 million Venus Protocol assets in BNB Chain exploit, CryptoRank. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 25by ToTo BugelmanNewcomer.jpeg) Crime
Hackers Leverage Ethereum's EIP-7702 Exploit to Target WLFI Token Holders
Holders of the World Liberty Financial (WLFI) governance token are currently falling victim to a sophisticated phishing exploit that leverages Ethereum's EIP-7702 upgrade. This vulnerability allows malicious actors to pre-plant compromised addresses in victim wallets, enabling them to quickly seize newly deposited tokens, including WLFI. Yu Xian Key Takeaways Hackers are exploiting Ethereum's EIP-7702 upgrade, introduced with the Pectra upgrade, to steal WLFI tokens. The exploit involves pre-planting a hacker-controlled address in victim wallets, often after private key leakage through phishing. Victims report losing significant amounts of WLFI, with some struggling to transfer remaining tokens due to the risk of immediate theft. The EIP-7702 Exploit Explained Ethereum's EIP-7702, designed to streamline user experience by allowing external accounts to temporarily act as smart contract wallets for batch transactions, has an exploitable flaw. Security experts, including SlowMist founder Yu Xian, have identified that hackers are using this upgrade to their advantage. The process typically begins with the leakage of a victim's private key, often through phishing attempts. Once the private key is compromised, the attacker can pre-plant a malicious delegate smart contract into the victim's wallet. When the victim deposits tokens, such as WLFI, into this compromised wallet, the hacker's contract can automatically transfer the assets away, often before the user can react. Yu Xian WLFI Token Holders Under Attack The World Liberty Financial (WLFI) token, which recently began trading, has become a target for these attacks. Reports indicate that users who participated in the WLFI presale, which required using the same wallet that joined the whitelist, are particularly vulnerable. Some users have described a frantic race against hackers to move their WLFI tokens to secure wallets, even finding that the gas fees for transactions could be instantly stolen. Many are left with a significant portion of their WLFI trapped in compromised wallets, fearing immediate loss once any remaining tokens are accessible. Broader Scam Landscape and Warnings Beyond the EIP-7702 exploit, the WLFI launch has also seen numerous other scam attempts, including fake smart contracts designed to mimic legitimate projects. The WLFI team has issued warnings, emphasizing that they do not contact users via direct messages on any platform and that official support is only available through designated email channels. They urge users to be vigilant against fraudulent communications claiming to be from the WLFI team. Sources WLFI Holders Targeted as Hackers Use Ethereum’s EIP-7702 Exploit, Cointelegraph. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 24by ToTo BugelmanNewcomer.jpeg) Crime
Crypto Hacks Skyrocket: August Sees $163 Million Lost
The cryptocurrency industry experienced a significant surge in security breaches during August, with total losses mounting to $163 million. This represents a 15% increase compared to July's losses of $142 million, highlighting a growing trend of cyber threats targeting digital assets. PeckShieldAlert Key Takeaways August witnessed approximately 16 major crypto exploits, resulting in substantial financial losses. The Turkish crypto exchange BtcTurk was a victim of a major hack, losing over $50 million, marking its second significant breach in just over a year. A single incident involving a private Bitcoin investor accounted for a massive $91 million loss due to social engineering tactics. August's Major Exploits August proved to be a challenging month for crypto security, with several high-profile incidents contributing to the overall loss of $163 million. The data, compiled by PeckShield, indicates a concerning escalation in the frequency and severity of these attacks. The Turkish cryptocurrency exchange BtcTurk suffered a significant blow, losing over $50 million in assets. This incident is particularly alarming as it marks the second major breach for the exchange within a little over a year, following a $54 million hack in June 2024. Perhaps the most devastating single event of the month involved a private Bitcoin investor who lost a staggering 783 BTC, valued at approximately $91 million. This loss was attributed to a sophisticated social engineering attack, underscoring the vulnerability of individual investors to such tactics. Other notable incidents that contributed to August's total losses include: Odin.fun: $7 million BetterBank.io: $5 million CrediX Finance: $4.5 million The Ongoing Battle Against Hackers These figures underscore the persistent challenges faced by the crypto industry in its ongoing struggle against cybercriminals. Experts have previously described the situation as an "endless war" with hackers, emphasizing the need for continuous innovation in security measures and user awareness. The increasing financial impact of these breaches serves as a stark reminder for both platforms and individual users to prioritize robust security practices. Sources Потери от взломов криптопроектов в августе достигли $163 млн, ForkLog. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 26by ToTo BugelmanNewcomer.jpeg) Crime
Cred Executives Jailed for $150 Million Crypto Fraud Scheme
Two former executives of the failed crypto lending platform Cred have been sentenced to federal prison for their roles in a $150 million fraud scheme. Daniel Schatt, the former CEO, received a 52-month sentence, while former CFO Joseph Podulka was sentenced to 36 months. Both men had previously pleaded guilty to wire fraud conspiracy charges. Key Takeaways Former Cred CEO Daniel Schatt sentenced to 52 months in prison. Former Cred CFO Joseph Podulka sentenced to 36 months in prison. The executives pleaded guilty to wire fraud conspiracy. The scheme defrauded over 440,000 customers, leading to losses exceeding $150 million. Sentences reflect accountability for executive misconduct in the crypto industry. The Fraudulent Scheme Daniel Schatt and Joseph Podulka admitted to misleading Cred customers about the company's financial health and lending practices. They falsely assured investors about the safety and collateralization of their funds, while secretly funneling approximately 80% of customer assets into high-risk microloans through an affiliated Chinese company, MoKredit. This firm specialized in unsecured loans to Chinese gamers. When the crypto market experienced a downturn in 2020, Cred could not meet its margin calls and faced insolvency. Despite knowing the company's precarious financial state, the executives continued to solicit new customers and discourage withdrawals, presenting an "unreasonably positive and thus misleading portrayal" of the business. Customer Losses and Legal Consequences The collapse of Cred resulted in significant losses for over 440,000 customers, with initial reported losses of up to $150 million. However, the U.S. Department of Justice noted that the value of these assets has since climbed to over $783 million. In their plea agreements, Schatt and Podulka acknowledged that their actions led to losses between $65 million and $150 million for users. Senior U.S. District Judge William Alsup handed down the sentences, emphasizing the importance of executive accountability in the burgeoning crypto sector. Legal experts suggest these sentences set new precedents, weighing factors such as loss amount, role in the offense, and acceptance of responsibility. Both executives are also ordered to pay $25,000 fines and will serve three years of supervised release after completing their prison terms. A restitution hearing is scheduled for October 7. Sources Former Cred Execs Sentenced to Federal Prison For $150M Crypto Fraud, Decrypt. Ex-Cred execs plead guilty to wire fraud over $150M crypto collapse, Cointelegraph. Ex-Cred execs plead guilty to wire fraud over $150M crypto collapse — TradingView News, TradingView. Executives of bankrupt crypto lender Cred plead guilty to $150M wire fraud, Cryptopolitan. Ex-Cred Executives Plead Guilty to $150M Crypto Fraud Scheme, Decrypt. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 24by DarshitaNewcomer Crime
Indian Court Delivers Life Sentences in Landmark Bitcoin Extortion Case
An Indian anti-corruption court has handed down life sentences to 14 individuals, including 11 police officers and a former legislator, for their roles in a 2018 kidnapping and Bitcoin extortion scheme. The group was found guilty of criminal conspiracy, kidnapping for ransom, illegal detention, and assault, marking a significant judicial stance against corruption involving public servants. DeshGujarat Key Takeaways Fourteen individuals, including 11 police officers and a former MLA, received life sentences. The case involved the kidnapping and extortion of a Surat-based businessman for Bitcoin in 2018. Convicted officers were also found guilty under the Prevention of Corruption Act. The court issued perjury notices to 25 witnesses who turned hostile during the trial. The Extortion Scheme Unveiled The case dates back to February 2018 when businessman Shailesh Bhatt was abducted and illegally detained. Bhatt had reportedly recovered a significant amount of Bitcoin after investing in a now-defunct cryptocurrency firm. Learning of this recovery, former Amreli district superintendent of police Jagdish Patel and ex-MLA Nalin Kotadiya allegedly orchestrated the kidnapping. Bhatt was reportedly beaten and coerced into admitting he held 752 Bitcoin, with 176 Bitcoin stored by an associate, Kirit Paladiya. The kidnappers extorted 34 Bitcoin, valued at approximately $150,000, from Bhatt after an initial deal for a larger sum fell through. The victim later filed a complaint with the Union home ministry, initiating a criminal investigation that led to the arrest of 15 individuals. Judicial Proceedings and Verdict Special Judge B.B. Jadav presided over the trial in Ahmedabad, where the prosecution presented 173 witnesses. However, 92 witnesses turned hostile, leading the court to issue perjury notices to 25 of them for potentially obstructing justice. The court emphasized the need to curb widespread corruption with a strong hand, stating that the verdict carried significant weight. All 11 police officials, including former IPS officer Jagdish Patel, were convicted under the Prevention of Corruption Act for misconduct. The court also ordered the confiscation of gold ornaments seized from SP Patel. The sentencing serves as a stern warning against the misuse of public office for personal gain and highlights the challenges law enforcement faces with digital asset-related crimes. Broader Implications and Ongoing Investigations The judgment has sparked discussions about the intersection of traditional criminal activities and cryptocurrencies. While the 14 were sentenced, the victim, Shailesh Bhatt, is also facing charges for alleged money laundering and kidnapping related to his own efforts to recoup his investment. A separate case is also pending against Bhatt's business partner and a CBI inspector. Sources Indian Court Sentences 14 to Life in Bitcoin Extortion Case, Cointelegraph. 14 sentenced to life imprisonment in Indian bitcoin extortion case, including 11 police officers, The Block. Bitcoin extortion case: Ex-BJP MLA, ex-SP among 14 handed life | Ahmedabad News, The Times of India. Indian court sentences former police officers to life for crypto extortion, Cryptopolitan. Life for Ex-MLA and Police in Bitcoin Extortion Scandal Signals Judicial Warning, AInvest. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 25by ToTo BugelmanNewcomer Crime
US Banks Facilitated $312 Billion in Laundering, Critics Point to Crypto's Unfair Scrutiny
A recent report reveals that U.S. banks moved a staggering $312 billion for Chinese money launderers between 2020 and 2024. This revelation comes as cryptocurrency continues to face intense scrutiny from politicians, despite evidence suggesting traditional financial systems handle a far greater volume of illicit funds. Nate Geraci Key Takeaways U.S. banks processed an estimated $312 billion in illicit funds for Chinese money laundering networks from 2020 to 2024. This activity averages over $62 billion annually, highlighting the scale of traditional finance's involvement in money laundering. Critics argue that cryptocurrency is unfairly targeted for illicit activities, while the vast majority of money laundering occurs through fiat channels. The Scale of Traditional Finance Laundering According to a U.S. Financial Crimes Enforcement Network (FinCEN) advisory, over 137,000 Bank Secrecy Act reports were analyzed. The findings indicate that Chinese money laundering networks have established a significant connection with Mexico-based drug cartels. These cartels require laundering services for their U.S. dollar drug proceeds, while Chinese gangs seek U.S. dollars to bypass China's currency controls. FinCEN Director Andrea Gacki stated that these networks launder proceeds for drug cartels and are involved in other substantial underground money movement schemes globally. Beyond drug money laundering, these Chinese gangs are implicated in human trafficking, smuggling, healthcare fraud, and elder abuse. The report also noted $53.7 billion in suspicious real estate transactions linked to these activities. Crypto's Unfair Reputation Despite these findings, cryptocurrency is frequently singled out by pro-banking politicians, such as Senator Elizabeth Warren, for its potential use in money laundering. Warren has previously called for tougher regulations on digital assets, citing their use by "bad actors." However, the FinCEN figures underscore a less-discussed reality: the bulk of money laundering does not involve cryptocurrency. Globally, the United Nations Office on Drugs and Crime estimates that over $2 trillion is laundered annually. In contrast, Chainalysis data suggests that illicit crypto volumes over the past five years totaled approximately $189 billion. Experts like Angela Ang, Head of Policy and Strategic Partnerships at TRM Labs, noted that illicit activity represents a small fraction of the crypto ecosystem, estimated at less than 1% of overall crypto volume. She commented that FinCEN's findings align with a broader pattern where underground banking networks operate as a shadow financial system for organized crime, exploiting the seams of traditional banking systems. Fiat Channels Dominate Illicit Finance Chengyi Ong, Head of APAC Policy at Chainalysis, echoed this sentiment, emphasizing that criminals utilize any available vector, including both fiat and crypto, to move illicit value. The sheer size and opacity of the traditional financial system mean that the majority of illicit value is undeniably transferred through fiat channels. Ong also pointed out that while crypto does have money laundering issues, the transparency of public blockchains can make illicit activity more visible, potentially fueling a narrative that crypto is primarily used for crime, when it is simply another transfer mechanism. Zigram Sources Chinese Gangs Moved $312B Through US Banks Over Five Years, Cointelegraph. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 23by ToTo BugelmanNewcomer Crime
Crypto-to-Gold Laundering Scheme Busted: South Korean Man Arrested in Thailand
Thai authorities have apprehended a 33-year-old South Korean national, identified as Han, in connection with a sophisticated $50 million cryptocurrency-to-gold money laundering operation. The arrest, made at Bangkok's Suvarnabhumi Airport, is a significant development in the ongoing crackdown on cross-border financial crimes involving digital assets. Bangkok Post Key Takeaways A South Korean man, Han, was arrested in Thailand for allegedly laundering $50 million in cryptocurrency. The illicit funds were converted into gold bars as part of a large-scale call center investment scam. Thai police have arrested ten other individuals in connection with the scheme. The case highlights the growing trend of using digital assets for money laundering and the challenges in tracing such transactions. The Laundering Operation Unveiled The scheme, which began in early 2024, targeted victims through fraudulent online investment opportunities promising high returns of 30-50%. Scammers initially provided small payouts to build trust, but later blocked withdrawals, leaving victims with substantial financial losses. Han, who had previously studied in China and worked for a South Korean company specializing in crypto-to-gold conversions, allegedly oversaw accounts that processed approximately $47.3 million in USDT between January and March 2024. These funds were then converted into gold bars, with each transaction reportedly involving over 10 kilograms of gold, valued at around $1 million. Arrest and Investigation Han was apprehended under an arrest warrant issued in February 2025, following complaints filed by victims in February 2024. Thai police, in collaboration with the Technology Crime Suppression Division and the Immigration Bureau, intercepted him at the airport. His mobile phone, containing multiple crypto accounts linked to the laundering network, was seized as evidence. Han faces charges including fraud, computer crimes, money laundering, and involvement in a criminal syndicate. Ten other suspects, including alleged launderers and mule account holders, have also been arrested as part of the ongoing investigation. The Nation Broader Implications and Future Concerns This case underscores the increasing sophistication of financial crimes involving cryptocurrencies and the challenges authorities face in tracking and regulating these digital assets, especially when converted into tangible commodities like gold. The incident highlights the need for enhanced international cooperation and robust regulatory frameworks to combat cross-border crypto-related crimes. Authorities are continuing their investigation, believing more information will emerge regarding foreign partners and the recovery of stolen funds, aiming to clean up the crypto market and protect investors from fraudulent schemes. Sources South Korean Man Accused of Crypto Laundering Arrested in Thailand, Live Bitcoin News. Thai Police Arrest Korean Man in $50M Crypto-to-Gold Laundering Case, Cointelegraph. South Korean Man Arrested in Thailand Over $50M Crypto-to-Gold Laundering Scheme, AInvest. Thai Police Arrest South Korean in $50M Crypto-to-Gold Laundering Scheme, AInvest. Thai Police Arrest South Korean in $50M Crypto-to-Gold Laundering Scheme, AInvest. This article was created with support from AI-driven technology, drawing on multiple reputable sources. The final content has been thoroughly reviewed and edited by BlockzHub's editorial team to ensure accuracy, clarity, and coherence. Original reporting sources are credited whenever appropriate and as required. The opinions expressed in this article do not necessarily represent the official views or positions of BlockzHub. This article is intended for informational purposes only and should not be considered financial or professional advice. Investing involves risk, and you should consult a qualified financial advisor before making any investment decisions.
0 0.0 26by ToTo BugelmanNewcomer